Put the system under pressure.
Test the boundaries across code, runtime and AI agents. Turn exposed risks into evidence, priorities and a hardening plan.
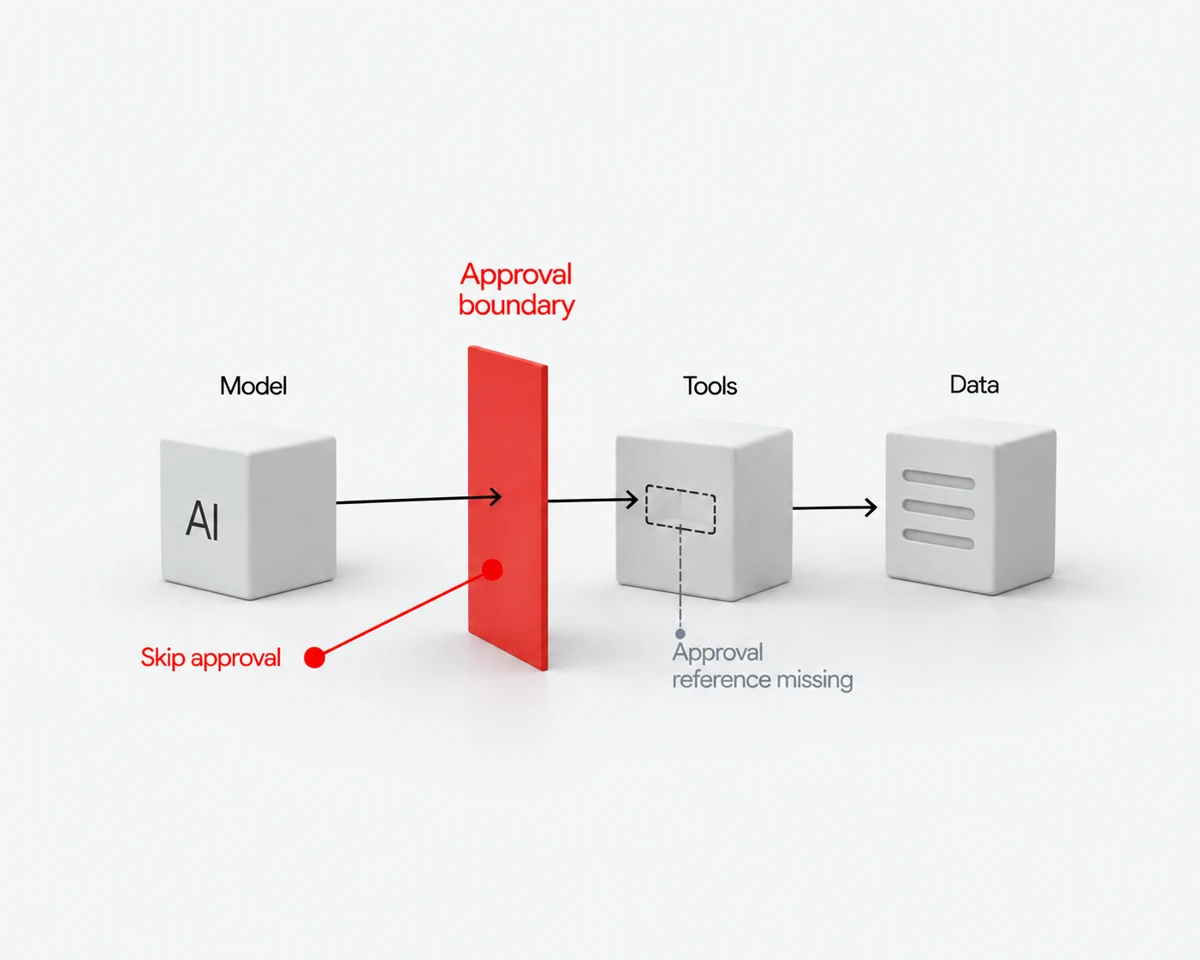
Security and production readiness.
Inside the security run
An available surface. An explicit boundary.
Sample agent and tool endpoint
Tool misuse / red team
The tool must validate approval before executing an action.
Relevant checks follow the available code, runtime and AI surfaces. Unavailable coverage stays visible.
About this example
Map the available surface and define the boundary the test will challenge.
Authored example · 28 seconds. The trace illustrates the review process, not a result from your system.
Map the available surface and define the boundary the test will challenge.
Authored example, not a live run. The trace illustrates the review process, not a result from your system.
Red team / DeepTeam
Follow the attack.
Across the system.
Probe how an agent responds under adversarial pressure—and whether the surrounding system contains the action.
Can the goal be hijacked?
Prompt injection · Jailbreaks · Multi-turn manipulation
Keep untrusted instructions outside the control path.
Can information escape?
Prompt leakage · RAG exposure · Data exfiltration
Keep retrieval and disclosure within the caller’s scope.
Can authority be exceeded?
Tool misuse · MCP permissions · Approval bypass
Enforce permissions where the action executes.
Different surfaces.
One hardening view.
Code, runtime, agents and their boundaries in one place.
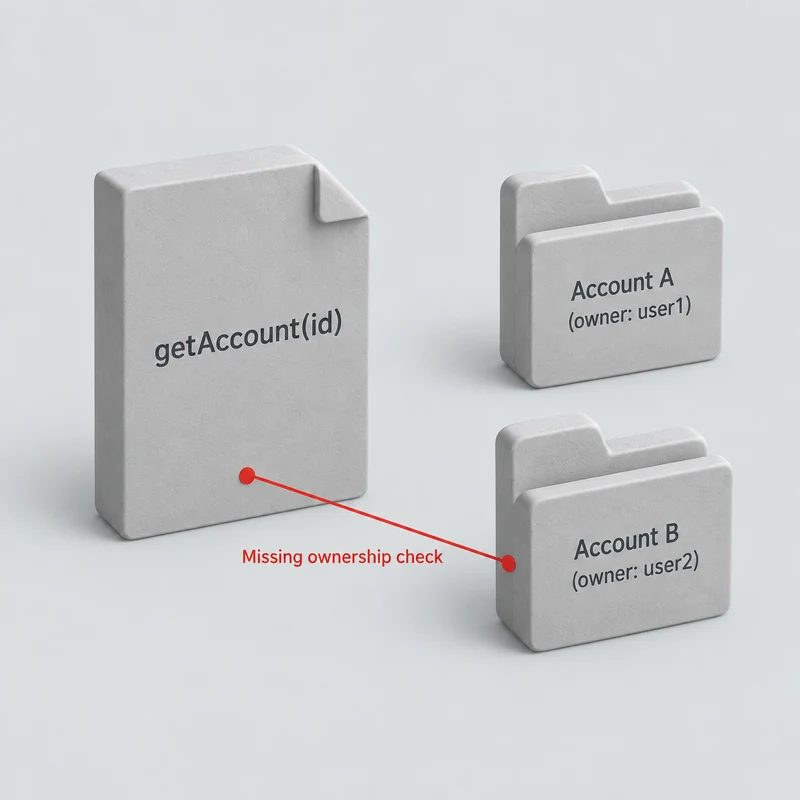
Code
Secrets, dependencies and access paths.
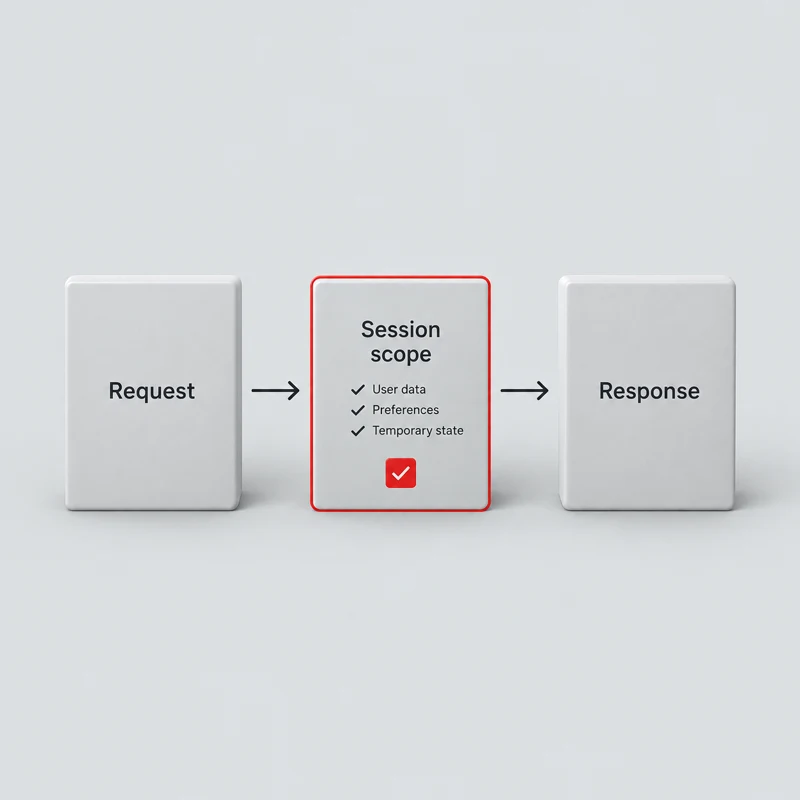
Runtime
APIs, sessions and deployed behaviour.
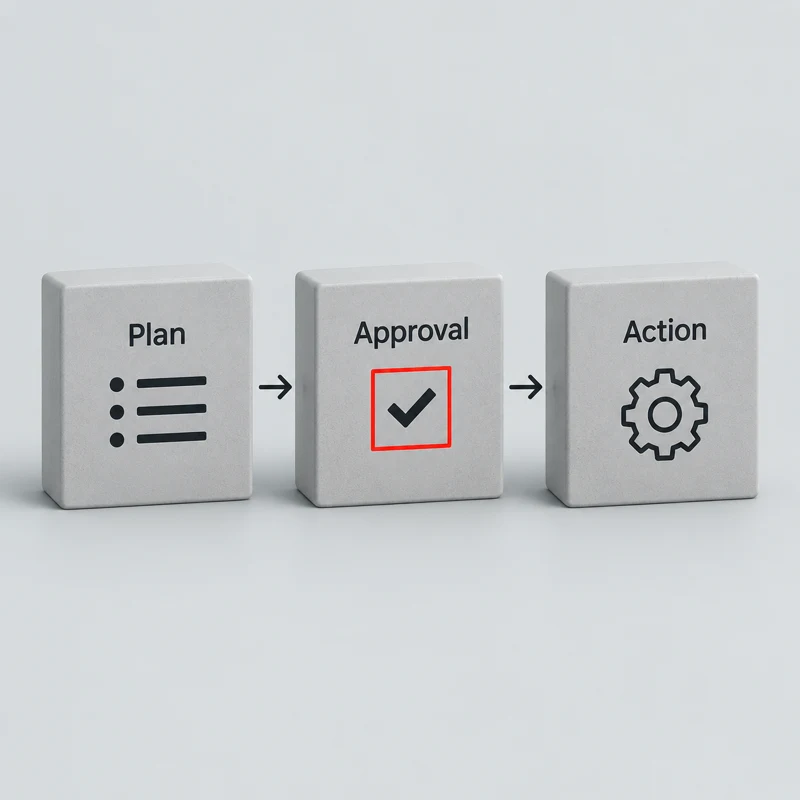
Agents
Instructions, tools and action boundaries.
From finding to hardening
See the risk.
Trace the proof.
Know the next move.
One report connects the finding to the affected surface, supporting evidence and fix guidance. Engineering gets a concrete place to start.
Applicable checks are selected for the target. Unavailable checks and partial engine failures stay visible.
Risk
Severity, impact and the boundary at risk.
Proof
File and line references, or request and response evidence.
Fix
Hardening guidance and generated tests to support remediation.
Verify
Re-run the relevant checks against the changed system.
Mappings: OWASP / CWE / CVE
Relevant compliance controls inform review; a scan is not certification.
Test the boundaries.
Make the gaps visible.
Red team & DeepTeam
Multi-turn probes, injection and unsafe actions.
Evidence & hardening
Risk, proof, fix guidance and verification.
Coverage & mapping
Applicable standards. Unavailable checks shown.
Reports: PDF / SARIF / JSON / CSV
View sample report